AI FOR SECURITY OPERATIONS
SoCMateYour AI Companion for
a

SoCMateYour AI Companion for
a
Faster, Smarter SOC
SoCMate works alongside your existing SOC stack to accelerate investigation, contextualize threats, and guide analysts from alert to action.
Book a Demo
Your SOC Has the Data.
SoCMate Finds What Matters.
SoCMate cuts through complex security data to help analysts investigate, correlate and qualify incidents faster.


WITHOUT SoCMate
-
1500+ tablesFind the right data
-
10,000+ fieldsIdentify what matters
-
Complex KQLBuild and refine queries
-
Multiple sourcesCorrelate evidence manually
-
Manual qualificationPiece together the incident
WITH SoCMate


 Ask in natural languageCorrelate the right dataQualified findingBuild context
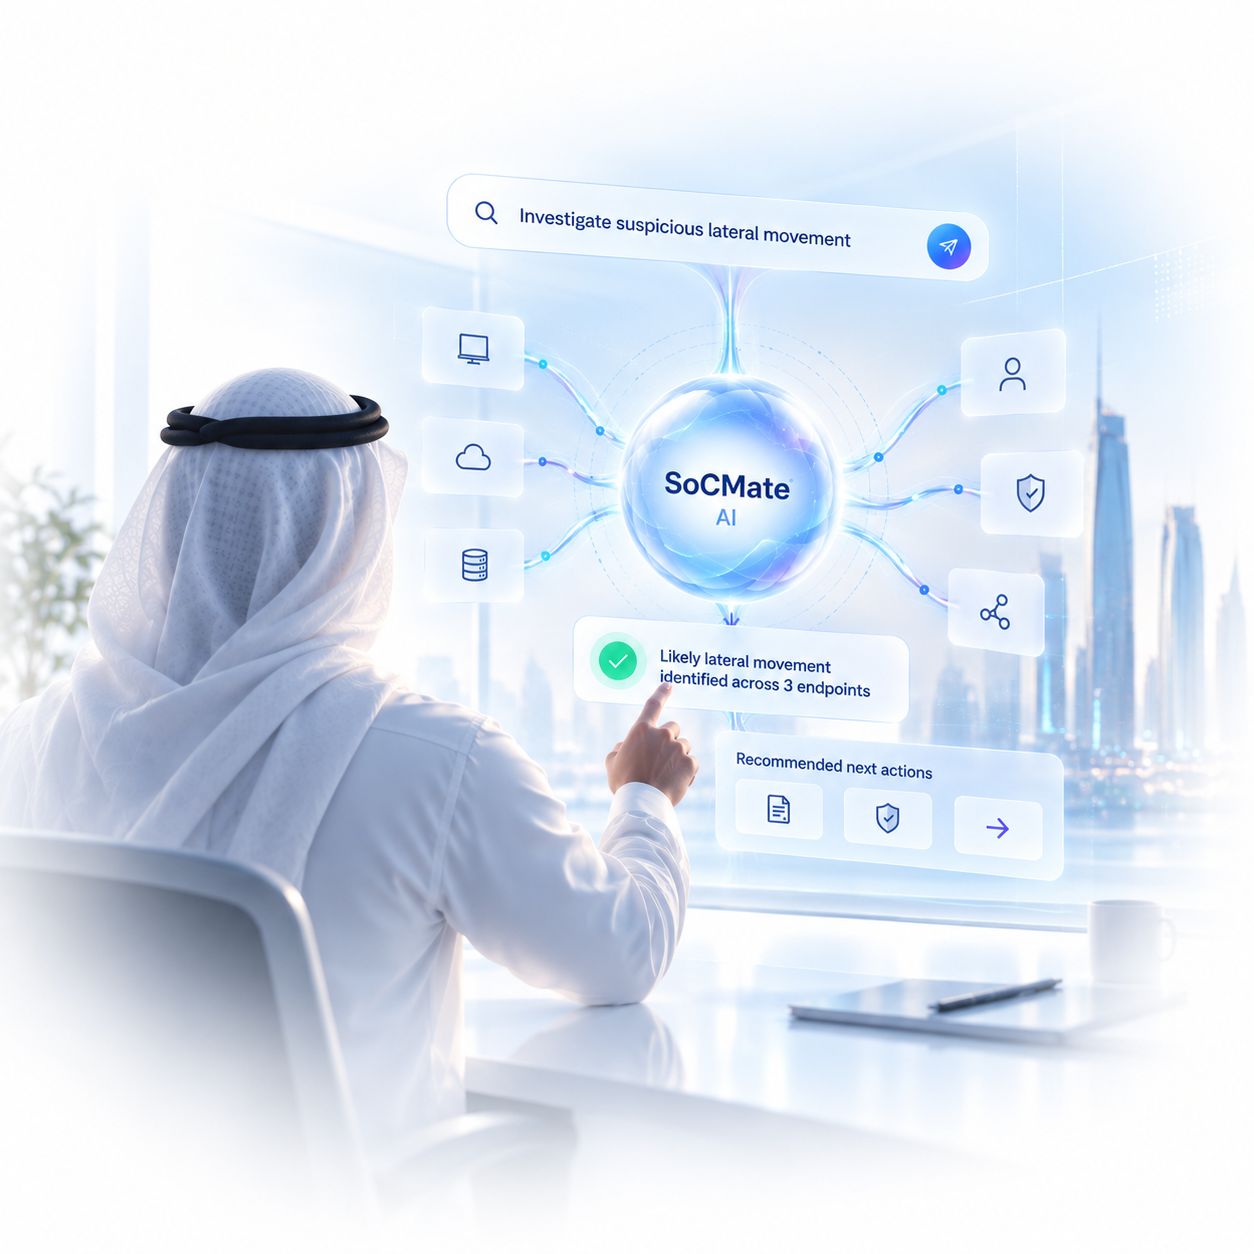
SoCMate interprets the analyst's question, pulls together the right security data and context, and turns it into a qualified finding with recommended next steps.

 Compresses
manual effort
Less searching. Less querying. Faster investigation.

More incidents investigated
Increase SOC throughput without adding equivalent analyst effort.

Less analyst fatigue
Reduce time spent searching, querying and correlating manually.

More time for higher-value work
Free analysts to focus on threat hunting, prioritization and response decisions.

Lateral
Movement
Movement
Data
Exfiltration
Exfiltration
2-4 hrs
4-8 hrs
8-10 min
8-10 min
without SoCMate
without SoCMate
with SoCMate
with SoCMate


Reclaimed
Analyst Time
Analyst Time
from repetitive
investigation work
investigation work

Lateral
2-4 hrswithout SoCMate8–10 minwith SoCMateData
Exfiltration
4-8 hrswithout SoCMate8–10 minwith SoCMate
Reclaimed
Analyst Time
from repetitive
investigation work
More incidents investigated
Increase SOC throughput without adding equivalent analyst effort.
Less analyst fatigue
Reduce time spent searching, querying and correlating manually.
More time for higher-value work
Free analysts to focus on threat hunting, prioritization and response decisions.
How SoCMate Works
From natural-language question to contextualized finding and next action in one investigation flow.


Ask
Start with a natural-language question instead of manually searching schemas or writing complex KQL.


Investigate
SoCMate identifies relevant security data, builds the required queries and follows the investigation path across sources.


Understand
It correlates historical, behavioural and incident context to clarify what happened and why it matters.


Act
SoCMate recommends the next step and can automate non-critical actions while critical decisions stay human-controlled.
Scale investigation capability without scaling analyst workload.
OPERATIONAL ADVANTAGE
More Investigation Power.
Less Analyst
Overhead.
SoCMate reduces the manual expertise and effort required to investigate incidents, helping teams work more consistently across skill levels.
Deep KQL
expertise required Investigate with
natural-language prompts
expertise required
Investigate with
natural-language promptsReduce dependence on specialist query knowledge.
High
cognitive loadLet SoCMate identify
relevant data and context
cognitive load
Let SoCMate identify
relevant data and contextSpend less effort navigating schemas and correlating results.
Slow movement
from alert to findingUse guided investigation and real-time context
from alert to finding
Use guided investigation and real-time contextHelp analysts reach qualified decisions faster.
Static reports limit collaborationShare investigation
history and qualified reports
Share investigation
history and qualified reportsLet stakeholders continue from the same context.
The result: more consistent investigations across analyst skill levels.
See What SoCMate Can Do for Your SOC
Explore how agentic investigations can reduce investigation time, analyst effort and operational complexity.
Book a SoCMate Demo
Get Expert Advice
Get in touch
Our dedicated team is committed to providing you with prompt and personalized support. Feel free to reach out to us, and we'll get back to you as soon as possible.