01

Missing Baseline
Most SAP security programs stall because nobody can say, with evidence, where the landscape stands.
Build a clear, evidence-based view of risk across your SAP environment. Paramount evaluates governance, S/4HANA, BTP, Fiori and applications against recognized frameworks and regional regulations, then prioritizes remediation.
Start your SAP Security Assessment
SAP remediation needs an evidence-based view of risks across authorizations, RFC, gateway trust, and HANA. An SAP-specific assessment provides the baseline to prioritize action and investment.
Most SAP security programs stall because nobody can say, with evidence, where the landscape stands.

Generic scanners and SOC tooling do not understand SAP's authorization model, RFC and gateway trust, or HANA-layer risks.

Findings from generic scanners and SOC tools rarely provide a defensible SAP security baseline or a clear business case for investment.
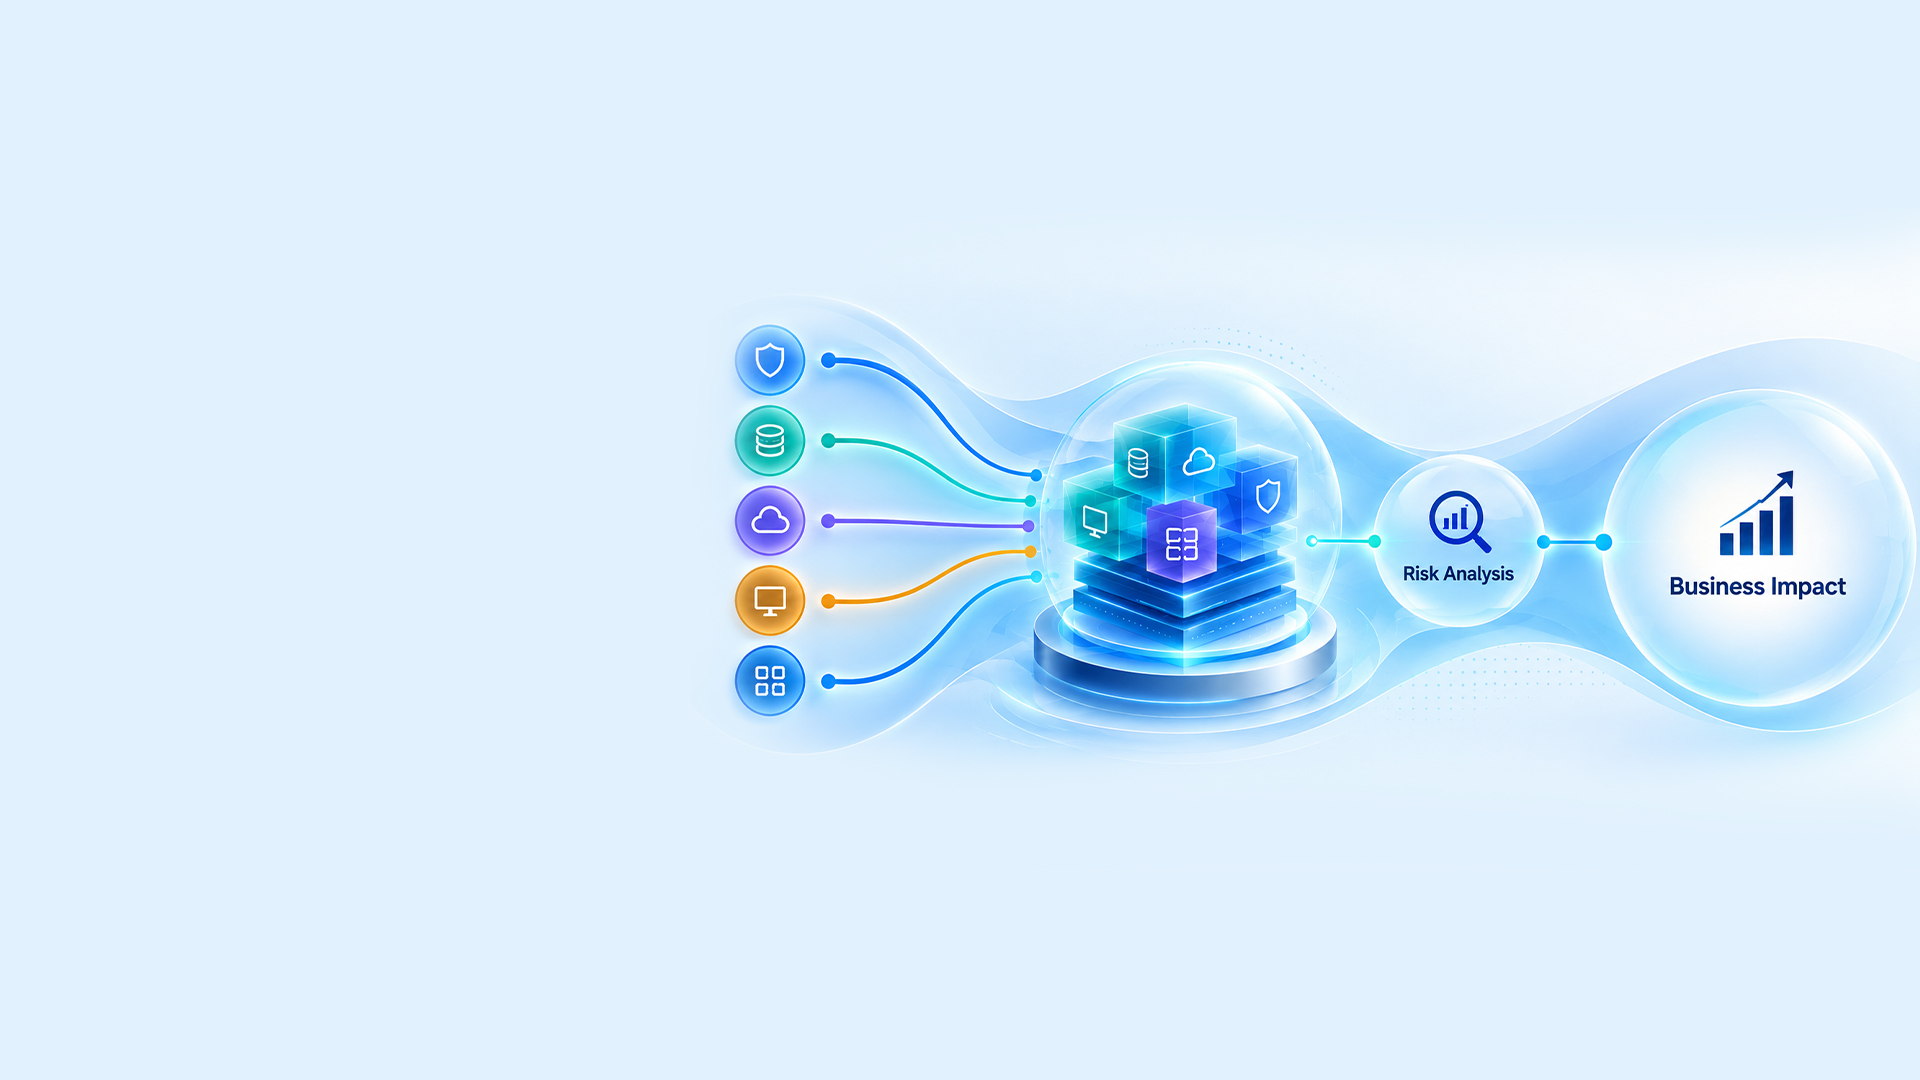
Paramount connects evidence across the four layers of the SAP Secure Operations Map to show where the organization stands, what needs attention first and where security investment should be prioritized.

Review authorizations, business processes, Fiori apps, custom code, privileged access, SoD challenges, application interfaces and data access to uncover application-level risk

Evaluate SAP platforms, databases, connectivity, system security configurations and interfaces for weaknesses that could increase technical exposure

Assess governance, ownership, skills, roles and responsibilities, security policies, compliance and regulatory alignment to identify gaps in how SAP security is managed
Assess change management, patching, monitoring and operational security practices to identify gaps in day-to-day security
Different SAP risks require different assessment scopes. Choose an enterprise-wide posture review, transformation-focused assurance, or an application-layer security assessment.
Build a landscape-wide view of SAP security maturity across governance, applications, infrastructure, privileged access, SoD, threat visibility, and operations.
Establishing a baseline, benchmarking maturity and defining a security roadmap.
Paramount delivers a benchmark-driven evaluation of SAP governance, technical controls, processes and people, measured against the SAP Secure Operations Map, NIST CSF, ISO 27001 and regional baselines including SAMA CSF and NCA ECC.
A defensible SAP security baseline for governance, regulatory reporting and investment decisions.
Gaps resolved in 30-90 days
Basis, Security, GRC, and business process owners

Policies, change management, patching cadence and segregation-of-duties frameworks

Organization, Application, Infrastructure and Environment layers

Preparing for a SAMA cybersecurity assessment

Consolidating SAP landscapes after an acquisition

Giving the CISO an evidence-based view of SAP risk

Building a first structured SAP security roadmap
Paramount assesses S/4HANA across on-premise, private-cloud and public- cloud environments, together with SAP BTP, to identify inherited ECC weaknesses, excessive privileges, insecure configurations and cloud connectivity risks before they move into production.
Greater confidence that the transformed SAP environment is ready to go live securely.
Go-live ready security view
S/4HANA on-premise, private cloud, public cloud and SAP BTP
HANA roles, S/4HANA authorizations, Fiori role mapping and BTP role collections
Trust configurations, destinations, Cloud Connector and on-premise-to-cloud connections
Greenfield or Brownfield conversion
Security review before production go-live
Launching a new BTP service or extension application
Consolidating multiple BTP accounts across entities
Paramount reviews the application layer users depend on, including the Fiori launchpad, Fiori and UI5 applications, OData services, SAP Gateway, authentication flows and custom ABAP code, to identify access, service exposure and custom-code security risks.
Stronger application-layer security without disrupting the business functionality users depend on.
Application-layerassurance
Fiori launchpad, Fiori and UI5 applications, OData services and SAP Gateway
Authentication, session management, single sign- on and service authorization
Custom ABAP, Z-transactions, XSS, CSRF, IDOR, hardcoded credentials and SQL injection
Large-scale Fiori rollout
Custom application approaching go-live
Fiori apps developed by a systems integrator
Apps exposed to customers, suppliers or other users
One consistent evidence pack, regardless of assessment scope. Every assessment ends in three deliverables and one document that supports governance, regulatory reporting and investment decisions.
Decision-ready outputs that convert evidence into a sequenced remediation plan.
Severity, exposure and business impact
Domain-level scoring and priority hotspots
Control owners, timelines and remediation sequence
The same assessment pack supports three different conversations.
Control ownership and governance review
Framework-ready evidence and obligations
Business-friendly risk narrative
Technical findings translated into action.

Combines SAP Basis and technical knowledge with enterprise cybersecurity, risk and compliance experience to assess SAP security in context.

Maps SAP controls to relevant regional frameworks, including SAMA CSF, NCA ECC and OTCC, DESC, ADHICS, PDPL, ISR 2.0 and QCB requirements.

Connects technical findings with their potential impact on financial, operational and regulatory processes.


Translates assessment findings into practical recommendations that can guide remediation, hardening and continuous security improvement.

Plans workshops and technical reviews around critical operating periods, approved change windows and reporting cycles.

Brings together SAP technical expertise, regional regulatory understanding and local operating context to support more relevant security decisions.
WHY PARAMOUNT
Paramount combines enterprise AI strategy with cybersecurity experience across complex, regulated environments.
Customers
Cybersecurity
Experts
GCC banks
Supported
Government
Customers
Translate complex SAP security findings into the clarity leadership needs to make confident risk, investment and compliance decisions.
WHAT THIS GIVES YOU

A sharper understanding of exposure across your SAP landscape.

Evidence that supports governance, reporting and investment decisions.

Evidence that supports governance, reporting and investment decisions.
NEXT STEP
Start with a focused discovery discussion to identify the right assessment for your SAP landscape.
Book a discovery discussion
Our dedicated team is committed to providing you with prompt and personalized support. Feel free to reach out to us, and we'll get back to you as soon as possible.

Copyright ©2026 Paramount. All rights reserved


