Critical Security Notes Get Lost in the Backlog
Teams cannot easily determine which Notes apply to their components and exposure. Urgent fixes are deferred alongside routine updates.
Identify exploitable weaknesses across SAP Security Notes, configurations, interfaces, and custom code. Prioritize remediation around business dependencies and verify that each fix holds.
Assess Your SAP Exposure
SAP exposure extends beyond missing patches. Configuration drift, trusted connections, and custom code create weaknesses enterprise scanners cannot interpret.
Teams cannot easily determine which Notes apply to their components and exposure. Urgent fixes are deferred alongside routine updates.

Transports, upgrades, emergency changes, and manual administration can move parameters away from the approved baseline.

Overprivileged RFC destinations, permissive gateway rules, exposed APIs, and unrestricted OData services can extend access between systems.


Custom ABAP, SAPUI5/Fiori applications, and OData services can contain authorization weaknesses, hardcoded credentials, injection flaws, and unsafe input handling.

Unclear dependencies across interfaces, batch jobs, and business processes cause teams to postpone remediation.


Conventional tools cannot fully interpret SAP components, Security Notes, transactions, authorization objects, or trust relationships.


Start with the condition already creating risk. Each service examines a defined part of the vulnerability lifecycle and produces a clear technical outcome.
Best for:Patch backlogs, pre-go-live reviews, recurring assessments, and post-incident validation.
SAP Security Notes, patch levels, profile parameters, gateway controls, RFC destinations, standard users, sensitive transactions, and exposed web interfaces.
A risk-rated findings report, CVSS-aligned scoring where applicable, supplemented by SAP-specific risk context, a prioritized remediation backlog, and step-by-step technical guidance.
Coverage spans SAP platforms, security configurations, privileged functions, interfaces, exposed services, and custom code.
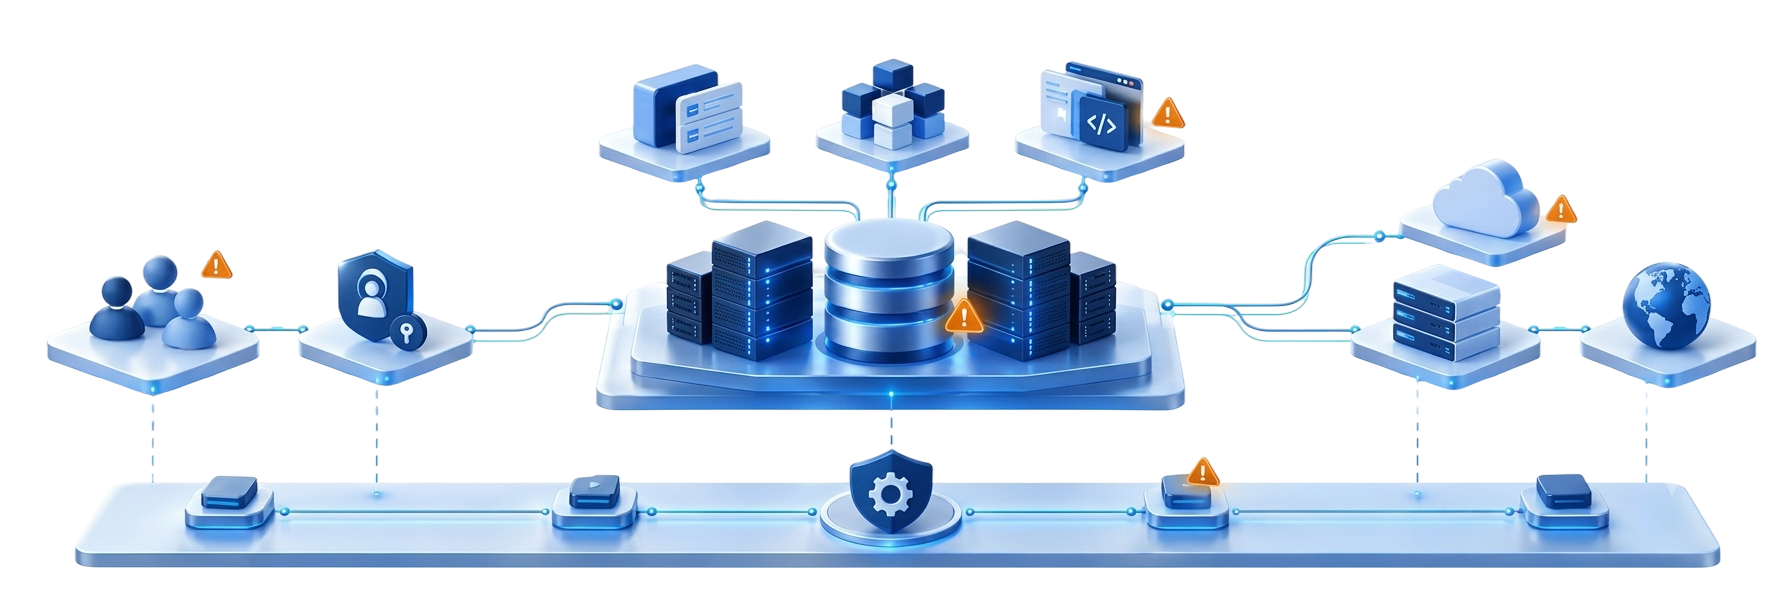
The report identifies the affected system, records the supporting evidence, explains the risk in context, and gives the responsible team a defined remediation action.
SAP, Basis, security, and business teams can use the same record to prioritize the issue, approve the change, complete the fix, and confirm closure through retesting.
REQUEST AN SAP VULNERABILITY ASSESSMENT

Ownership, change planning, and proof of closure.
Validate in QA, test dependencies, and deploy through an approved change window.
RETEST PENDING IMPLEMENTATION
Paramount combines SAP technical expertise with the remediation planning and operational controls required to close vulnerabilities safely.
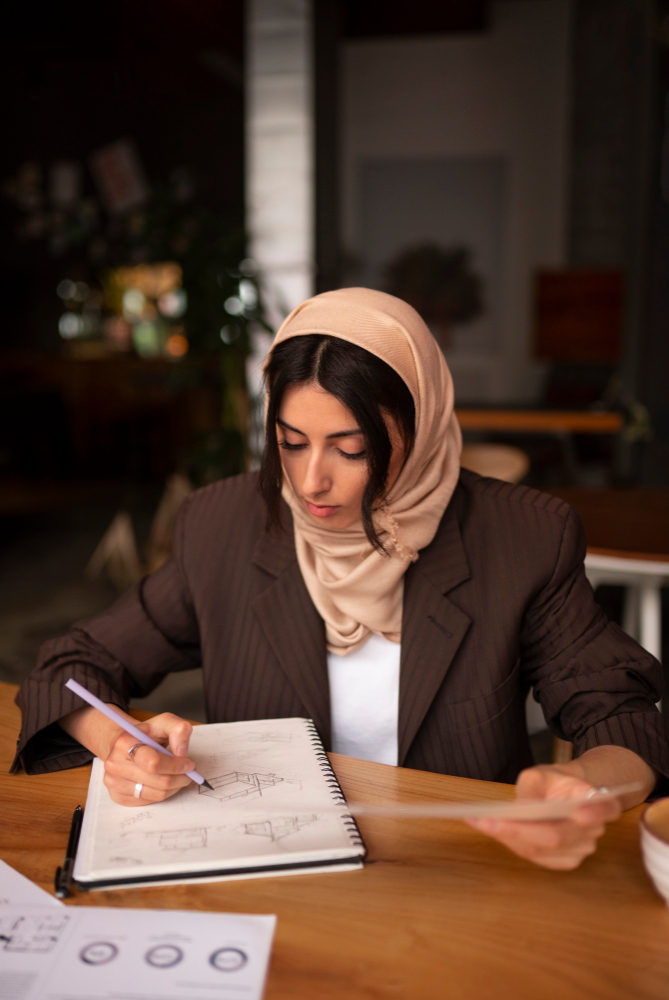
Automated checks are supported by manual analysis of SAP components, configurations, transactions, interfaces, and custom applications.
WHY PARAMOUNT
Paramount combines enterprise AI strategy with cybersecurity experience across complex, regulated environments.
400+
575+
24+
30+
Tell us what is driving the review. We will help define the systems, scope, and appropriate starting service.
Request an SAP Vulnerability Review
Our dedicated team is committed to providing you with prompt and personalized support. Feel free to reach out to us, and we'll get back to you as soon as possible.

Copyright ©2026 Paramount. All rights reserved