Why Enterprise Compliance Controls
Break Down in SAP
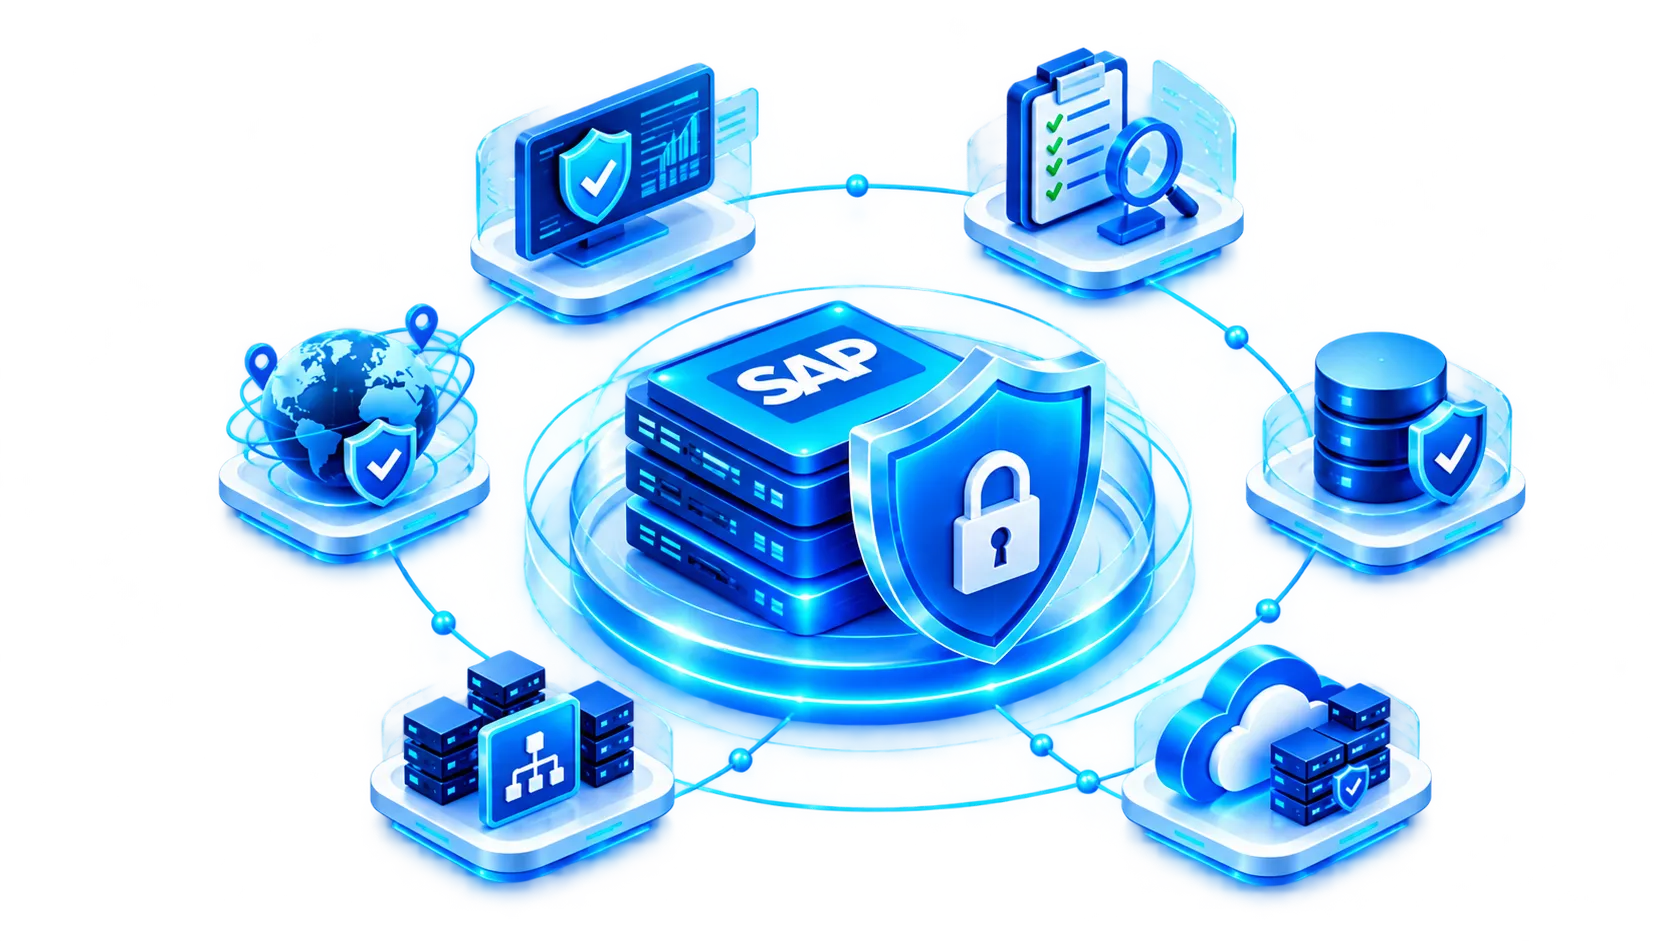
Effective Security Audit Services must test how controls operate inside SAP. Policies cannot prove that access, changes, logs, and data flows are controlled in practice.

SAP Controls Have No Supporting Evidence
Control requirements sit in policies and spreadsheets, while the relevant SAP configurations, approvals, workflows, and system records remain unlinked.
SoD Conflicts Lack Valid Mitigation
Conflicts remain open because mitigating controls are too broad, approvals expire, and exceptions are not reassessed.

Firefighter Sessions Go Unreviewed
Emergency access logs exist, but business justification, activity review, and reviewer sign-off are completed late or missed entirely.

Transport Approvals Are Incomplete
Testing records, change approvals, transport requests, and production releases are stored separately, breaking the evidence trail.

Log Coverage Cannot Be Proven
Teams enable SM19/SM20 or HANA audit logs without proving scope, retention, review frequency, escalation, or investigation follow-up.
Cloud Control Ownership Is Unclear
RISE, BTP, HANA Cloud, and Cloud Connector leave specific controls with the customer, but legacy audit programs may not assign or test them.
Choose the Assurance Model
Your Audit Requires
Paramount's Security Audit Services and Compliance Services can support a defined audit or establish a recurring control- assurance cycle. Start with the pressure already affecting your SAP team.
01
Regulatory and Compliance Readiness Assessment
Best for:
Upcoming audits, regulator requests, go-live approvals, repeated findings, and new regulatory obligations.
What we assess:
Applicable requirements and the design, operation, ownership, and evidence of controls covering access, SoD, emergency access, changes, logging, patch governance, data flows, interfaces, and incident response.
What you get:
An SAP-to-control matrix, evidence register, readiness status, gap report, accountable owners, remediation timelines, and mock-audit preparation
02
Compliance Automation and Continuous Assurance
Best for:
Recurring evidence requests, multi-entity landscapes, manual control testing, and gaps that reappear between audit cycles.
What we Establish:
Evidence sources, control calendars, reviewer responsibilities, approval workflows, exception handling, remediation tracking, and recurring reporting.
What you get:
A repeatable evidence process, current control-status dashboard, exception register, overdue-action tracking, remediation status, and management reporting.
What We Review Across
Your SAP Control Environment
Each control is tested for design, operation, ownership, and supporting evidence.
01
Identity, Access, and SoD
What we test:
User access controls, privileged access, segregation of duties conflicts, and access recertification.
Evidence Reviewed
Recertification sign-offs, conflict reports, approvals, exceptions, and provisioning records.
02
Privileged and Emergency Access
What we test:
Assignment, authorization, expiry, activity review, and escalation.
Evidence Reviewed
Firefighter logs, access requests, business approvals, reviewer records, and exceptions.
03
Change and Transport Governance
What we test:
Testing, release approval, segregation, and emergency changes.
Evidence Reviewed
Transport logs, test results, change records, and production approvals.
04
Audit Logging and Review
What we test:
Log coverage, retention, review, escalation, and investigation.
Evidence Reviewed
SM19/SM20 settings, HANA audit trails, SAP security monitoring records, and incident tickets.
05
Patch and Configuration Governance
What we test:
Patch review, baseline deviations, exceptions, and revalidation.
Evidence Reviewed
Patch reports, risk acceptances, approved baselines, and post-change checks.
06
Data, Interfaces, and Cloud Controls
What we test:
Data location, cross-border flows, RFCs, APIs, Cloud Connector, BTP services, and third-party ownership.
Evidence Reviewed
Data-flow maps, interface inventories, responsibility records, and third-party approvals.
Map the Right Requirements to
the Right SAP Evidence
Select a country to see the requirements that may apply and the SAP evidence needed to support them.
1
2
3
01. Saudi Arabia
NCA Essential Cybersecurity Controls 2:2024, relevant cloud or critical-systems controls, SAMA requirements for regulated financial institutions, and applicable Saudi PDPL obligations.
Each mapping records the requirement, SAP control, evidence source, owner, test result, gap, and remediation status.
02. UAE and Dubai
DESC Information Security Regulation for Dubai Government entities, CBUAE requirements for regulated financial institutions, ADHICS for relevant Abu Dhabi healthcare entities, and applicable UAE data-protection requirements.
Each mapping records the requirement, SAP control, evidence source, owner, test result, gap, and remediation status.
03. Qatar
The National Information Assurance Standard, QCB technology-risk requirements for regulated institutions, and relevant data-protection obligations.
Each mapping records the requirement, SAP control, evidence source, owner, test result, gap, and remediation status.
- ISO/IEC 27001
- NIST CSF
- SOX/ITGC
- PCI DSS
- GDPR
Applicability depends on jurisdiction, sector, entity classification, data, and SAP deployment model.
See What an Audit-Ready SAP Control Record Looks Like
Give Auditors One Defensible Record
The control-evidence matrix shows what was tested, which evidence was reviewed, whether the control operated as expected, and who owns any gap. Internal audit, GRC, SAP security, and business owners can work from the same record before the formal review begins.
Request an SAP Audit Readiness ReviewIllustrative Control Record
Emergency Access Management
-
Requirement
Emergency privileged activity must be authorized, logged, and reviewed.
-
SAP control
Firefighter access requires approval before use and an activity review after the session ends.
-
Evidence reviewed
GRC access request, firefighter assignment, activity log, reviewer sign-off, and exception record.
-
Gap
Three of 25 sampled sessions did not receive a timely post-use review.
-
Risk
Emergency activity may remain unverified, limiting assurance over privileged changes made in SAP.
Required Action
Enforce the review deadline, complete missing sign-offs, and retest the affected sessions.
- OWNER SAP GRC Lead
- TARGET 30 days
- RETEST Pending remediation
Why Paramount for
SAP Security Audit Services
Paramount connects regulatory interpretation with the SAP teams, controls, and system evidence required to support an audit.
SAP-Specific Control Interpretation
Requirements are translated into controls across SAP roles, workflows, configurations, logs, transports, interfaces, cloud services, and operating processes.
Evidence Tested at the Source
Paramount reviews system configurations, records, approvals, logs, and representative samples to determine whether the control operated as expected.
Regional Scope Defined Upfront
The control set reflects the customer's jurisdiction, sector, entity classification, data, and SAP deployment model.
Findings Built for Closure
Each gap includes the evidence reviewed, audit implication, accountable owner, required action, target date, and retest status.
Connected SAP Security Solutions
Audit findings can feed into vulnerability management, access governance, hardening, threat detection, and recurring compliance assurance where further action is required.