From OT Blind Spots to Centralised Control: Securing 50+ Distributed Pipeline Sites with IBM QRadar

Summary

A pipeline infrastructure operator managing more than 50 remote OT sites was facing limited central visibility, high manual monitoring effort, and difficulty correlating security and operational events across distributed locations. With limited monitoring resources and a large OT footprint, the organisation needed a scalable way to monitor site activity, improve event detection, and reduce the time spent on manual checks.

Paramount assessed the customer’s OT and security infrastructure and implemented IBM QRadar Security Information and Event Management (SIEM) as the central monitoring platform. The solution brought OT, IT, network, and security signals into a unified monitoring layer by integrating SCADA systems, Nozomi sensors, OT switches, firewalls, engineering workstations, servers, and other network devices.

With centralised log collection, event correlation, dashboard-based monitoring, and OT-focused alert workflows, the customer gained a single view across its distributed infrastructure. Based on client-provided estimates, the solution reduced manual monitoring eort by up to 70%, saved around 4–6 hours per day for the monitoring team, and reduced operational monitoring cost pressure by an estimated 25–35%.

Icon The Challenge

The operator was managing a large distributed OT environment with limited monitoring resources. Without a centralised monitoring layer, visibility across site-level activity, device behaviour, security events, and operational changes was fragmented.

  • Lack of centralised monitoring across IT and OT environments.
  • Limited visibility into site-level security, operational events, and device activity.
  • High manual monitoring effort across more than 50 remote OT sites.
  • Difficulty identifying and correlating incidents across distributed locations
  • Multiple devices and log sources spread across different sites
  • Limited audit visibility and change-monitoring discipline
  • Difficulty detecting rogue devices across distributed OT locations
  • Operational efficiency constrained by fragmented monitoring and resource limitations

Icon The Solution

Paramount conducted a detailed assessment of the customer’s OT and security environment and identified IBM QRadar SIEM as the appropriate platform for centralised monitoring.

  • Deployed IBM QRadar SIEM as the central monitoring platform
  • Integrated QRadar collectors and Nozomi sensors into the monitoring architecture
  • Connected SCADA systems, OT switches, firewalls, engineering workstations, servers, and other network devices
  • Enabled centralised log collection across distributed sites.
  • Configured event correlation to connect related operational and security signals
  • Built dashboards and alert workflows for OT monitoring
  • Fine-tuned monitoring and detection use cases around OT-specific risks
  • Created a single monitoring layer for all 50+ sites

Icon The Impact

The implementation helped the customer move from fragmented site-level monitoring to a centralised, correlation-led model for OT visibility.

  • Client-reported reduction of up to 70% in manual monitoring effort
  • Approximately 4–6 hours saved per day for the monitoring team, based on client-provided estimates
  • Faster incident investigation through centralised visibility and event correlation
  • Estimated 25–35% reduction in operational monitoring cost pressure.
  • Ability to monitor 50+ distributed OT sites centrally with limited resources.
  • Improved visibility across IT, OT, network, and security environments.
  • Stronger audit visibility and change-monitoring discipline.
  • Better coordination between operations, security, and infrastructure teams
Image

Overview

For organisations operating distributed OT infrastructure, visibility is both a security requirement and an operational control requirement. In a pipeline environment, site-level events, SCADA activity, engineering workstation behaviour, firewall activity, rogue-device entry, and operational changes need to be monitored consistently to reduce operational risk and support faster response.

The customer was operating more than 50 distributed OT sites, but monitoring remained fragmented. IT and OT environments were managed separately, and the team did not have a unified view of what was happening across remote locations. With limited manpower, the customer could not depend on manual monitoring or site-by-site checks to identify events quickly.

The organisation needed a scalable monitoring foundation that could bring OT, IT, network, and security signals into one environment. Paramount implemented an IBM QRadar-led SIEM solution that enabled centralised visibility, event correlation, dashboard-based monitoring, and faster investigation across the customer’s distributed pipeline infrastructure.

The Challenges

  • Limited Visibility Across 50+ Distributed OT Sites: The customer’s OT environment was spread across more than 50 remote sites. Each site included operational systems, network devices, firewalls, and engineering workstations. Without a centralised monitoring layer, visibility into site-level activity, system changes, device behaviour, and potential security events was limited.
  • Limited Monitoring Resources for a Large OT Footprint: The customer had limited IT and OT resources to monitor a large distributed environment. Manual monitoring across many sites consumed significant time and was dicult to scale. The organisation needed centralised monitoring without adding proportional manpower.
  • Fragmented IT and OT Monitoring: The IT and OT environments were managed separately, making it harder to connect security, network, and operational events. Without a unified monitoring layer and event correlation, the team had to spend more time investigating events manually.
  • Difficulty Detecting OT-Specific Risks: The customer needed to monitor OT-specific use cases such as SCADA activity, engineering workstation behaviour, abnormal site access, rogue-device activity, and operational changes. If an unauthorised device entered the network or an engineering workstation showed unusual activity, the customer needed that event to be detected and escalated quickly.
  • Change Monitoring and Audit Visibility Gaps: Operational changes were not always monitored consistently. This created gaps in audit visibility and made incident investigation more dicult. In an OT environment, poorly monitored changes can increase operational risk and complicate root-cause analysis.
  • High Alert Volumes and Monitoring Noise: The customer was receiving a high volume of alerts, many of which required better tuning and alignment with monitoring policies. With limited use-case tuning and insucient event correlation, the team had to spend significant eort separating meaningful events from routine activity.


The Solution

Paramount’s approach focused on helping the customer move from fragmented OT monitoring to centralised, correlation-driven visibility.

  • IBM QRadar SIEM Deployment: Paramount implemented IBM QRadar SIEM as the central monitoring platform for the customer’s
    distributed OT infrastructure. QRadar provided the foundation for centralised log management, event correlation, dashboarding, and real-time event monitoring across the OT environment.
  • QRadar Collectors and Nozomi Sensor Integration: QRadar collectors and Nozomi sensors were integrated into the monitoring architecture to bring site-level telemetry into a central environment. This allowed the customer to monitor distributed OT infrastructure more eectively without relying only on local checks at each site.
  • Integration of Critical OT and Network Systems: Paramount integrated multiple technologies and log sources into the QRadar environment, including:
    • SCADA systems
    • Nozomi sensors
    • OT switches
    • Firewalls
    • Engineering workstations
    • Servers
    • Security appliances
    • Other network devices
      This helped the customer bring operational, network, and security signals into a unified monitoring platform.
  • Centralised Log Collection and Event Correlation: The solution enabled log collection from distributed sites and allowed QRadar to correlate events across multiple systems. By connecting related events, the monitoring team could identify patterns, detect suspicious activity, and investigate incidents faster.
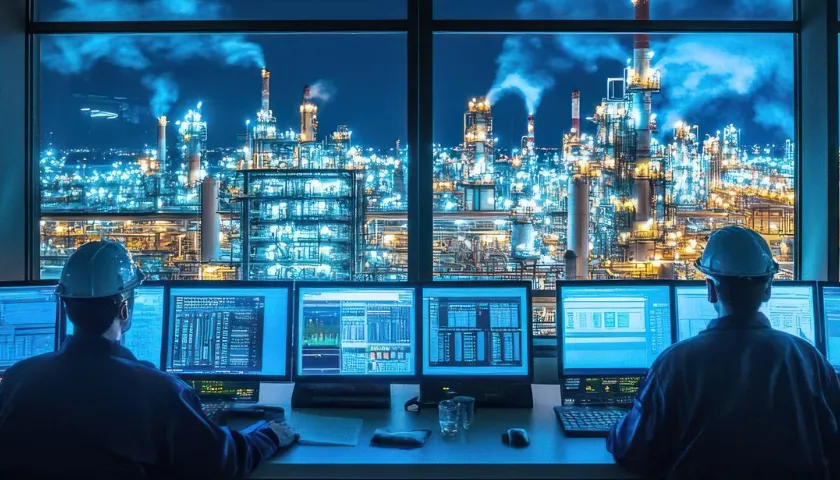
  • OT-Focused Monitoring Dashboards: Paramount created security monitoring dashboards and alert workflows tailored to the OT environment. These dashboards helped the team monitor site activity, device behaviour, security events, and operational anomalies from a single platform interface.
  • Fine-Tuned Use Cases for OT Monitoring: Paramount fine-tuned monitoring and incident-detection use cases around the customer’s operational risks. These included rogue-device detection, abnormal engineering workstation activity, site access anomalies, SCADA-related changes, firewall events, and other high-priority OT indicators.
Image

IBM QRadar Restores Control Through Centralised OT Visibility

Icon
Single-Pane-of-Glass Monitoring

IBM QRadar enabled the customer to monitor all 50+ sites from a central platform, reducing reliance on multiple isolated monitoring views and manual site-level checks.

Icon
Real-Time Event Monitoring and Correlation

By collecting and correlating events in near real time, QRadar helped the customer improve incident detection and reduce manual investigation effort

Icon
OT and IT Context in One Platform

The solution brought OT systems, IT systems, network devices, firewalls, engineering workstations, and security appliances into a unified monitoring environment. This improved coordination between operations, security, and infrastructure teams.

Impact of the Implementation

  • Client-Reported Reduction of Up to 70% in Manual Monitoring Effort

    Centralised dashboards, automated log collection, and event correlation reduced the need for manual monitoring across individual sites. This allowed the monitoring team to spend less time collecting information and more time investigating meaningful events.
  • Approximately 4–6 Hours Saved Daily for the Monitoring Team

    Based on client-provided estimates, the monitoring team saved around 4–6 hours per day through centralised monitoring, dashboard-based visibility, and event correlation.
  • Faster Incident Detection and Troubleshooting

    The customer was better positioned to detect abnormal activity, rogue devices, operational changes, and sitelevel security events faster. Centralised visibility also improved the efficiency of incident investigation and troubleshooting.
  • Estimated 25–35% Reduction in Operational Monitoring Cost Pressure

    By centralising monitoring and reducing dependency on additional manual eort, the customer reduced operational monitoring cost pressure by an estimated 25–35%.
  • Centralised Control Across 50+ Sites

    The organisation was able to monitor its distributed OT infrastructure centrally despite limited resources. This improved operational discipline and created a stronger foundation for future monitoring expansion.
  • Improved OT Security Visibility

    The implementation strengthened visibility across the OT environment by enabling real-time monitoring, event correlation, dashboarding, and use-case-driven detection.
Image
IBM QRadar

IBM QRadar provided the SIEM foundation for centralised log management, event correlation, real-time event monitoring, dashboard visualisation, and OT security analytics. For the customer, QRadar helped transform a fragmented, manpower-intensive monitoring model into a centralised and scalable security operation. It enabled the organisation to monitor distributed OT sites from a single platform, reduce manual eort, and improve incident detection across critical pipeline infrastructure.

Get Started

Why Choose Paramount as Your OT Security Monitoring Partner?

Paramount helps organisations modernise security monitoring across complex IT and OT environments. Its approach combines infrastructure assessment, SIEM deployment, log-source integration, use-case development, dashboarding, and operational fine-tuning.

For pipeline infrastructure operators, OT security monitoring is not only about detecting cyber threats. It is about improving control over distributed assets, reducing manual eort, strengthening audit visibility, and enabling faster response when site-level anomalies occur.

By combining IBM QRadar with Paramount’s OT security implementation expertise, the customer gained a scalable monitoring foundation that supports distributed operations, improves visibility, and strengthens security monitoring across more than 50 sites.

Download Case Study

Download Now
Paramount-Whatsapp