01. Detect
SecurityBridge surfaces SAP-specific threats and security-relevant activity.
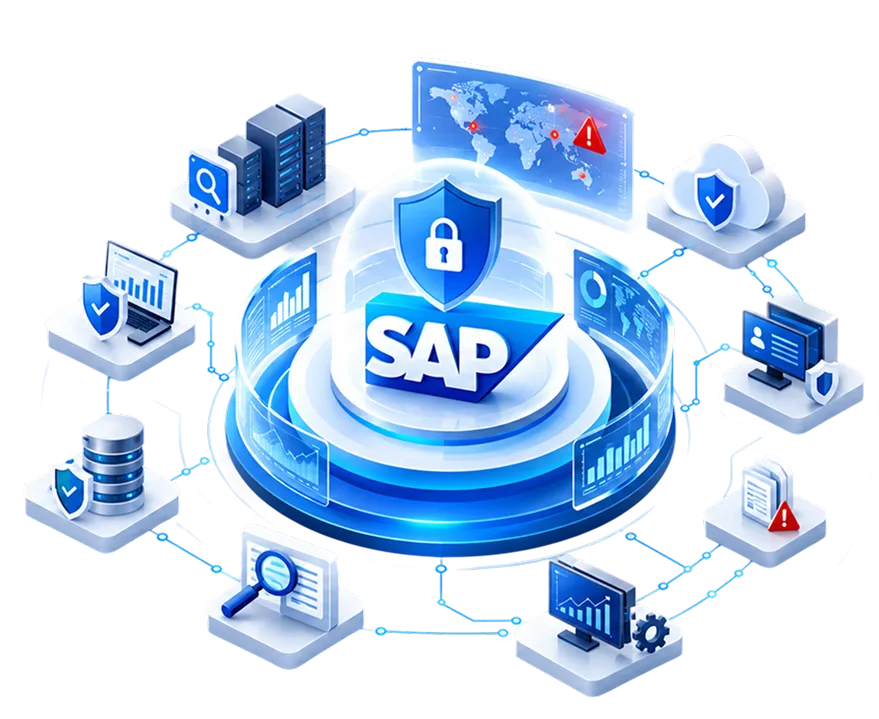
SAP threats do not always look like network intrusions.

A user posts an unauthorized journal entry that bypasses normal business controls.

An unusual RFC call reaches a sensitive SAP system or function.

A user initiates an unauthorized debug-and-replace session to alter application behavior.

A privileged user quietly changes a critical table behind the application layer.
Generic SIEM and EDR tools can collect SAP activity, but they may not interpret SAP's authorization model, transaction codes or application-layer logs well enough to understand what the activity means.? That can leave the systems running finance, supply chain and core operations among the least visible parts of the security stack.
Paramount brings continuous SAP threat detection and monitoring across users, applications, code and connected systems to surface suspicious activity, privilege abuse and security-relevant changes.

Detect anomalous activity and previously unseen attack patterns across SAP applications and databases.
Identify unusual activity involving privileged, emergency and firefighter accounts.

Scan ABAP code for vulnerabilities, malicious code and insecure development patterns.

Use SAP-specific detection rules maintained and updated without building detection logic in-house.

Continuously identify and prioritize SAP vulnerabilities based on severity and exploitability.

Contextualise findings against real exploitability to help reduce noise and focus investigation.
SecurityBridge adds SAP-specific context to to detected activity, helping your SOC understand what happened, why it matters and how to respond.
SecurityBridge surfaces SAP-specific threats and security-relevant activity.
Alerts are enriched with users, systems, applications and SAP activity.
Relevant events can flow into Microsoft Sentinel, Splunk, IBM QRadar and ServiceNow.
Alerts are enriched with users, systems, applications and SAP activity.
Prioritized findings enter existing investigation and remediation workflows.
Result: SAP monitoring becomes part of the wider security operation without creating a separate monitoring silo.
A SAP-native detection platform, operated through Paramount's monitoring expertise and SOC-ready workflows.
Designed for SAP environments where visibility must be continuous, contextual and easy to act on.
Integrating SAP threat data into an existing SOC and supporting continuous-monitoring expectations such as SAMA.
Running mixed ECC, S/4HANA, RISE and hybrid environments that need consistent visibility across the landscape.
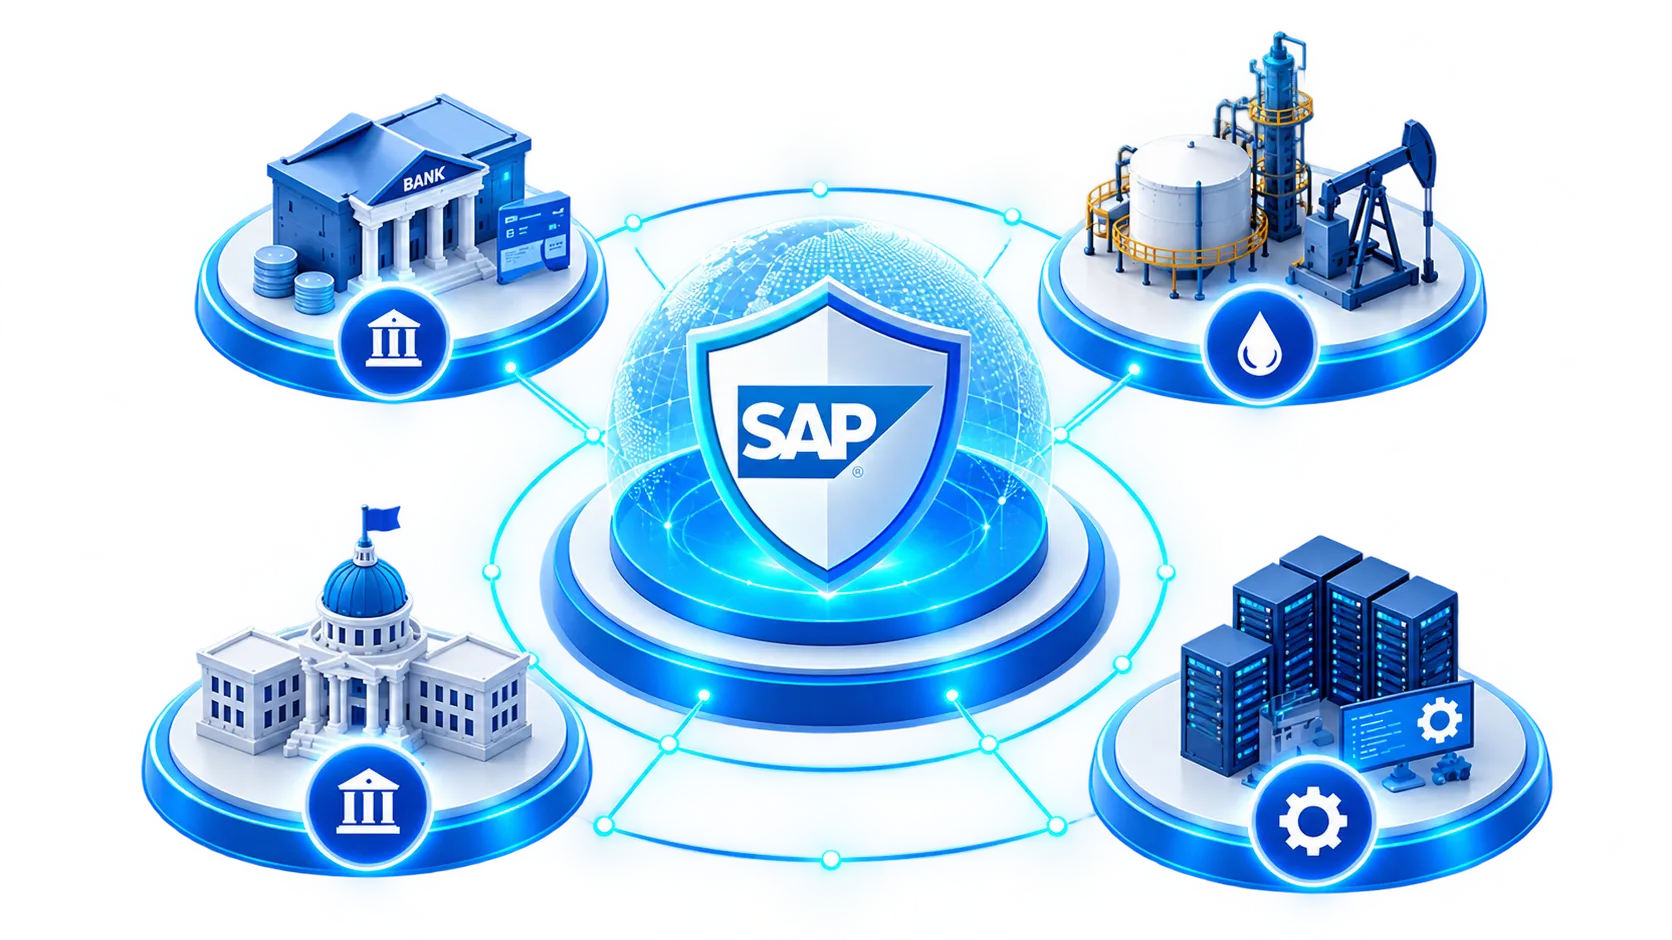
Strengthening continuous monitoring and security evidence for requirements such as NCA ECC and OTCC.
Managing extensive custom ABAP development where code, privilege and application-layer risks need closer monitoring.
Gain continuous visibility into the SAP activity that matters most to your business and security teams.
Monitor security-relevant SAP activity beyond periodic reviews.
Identify suspicious behavior while it is happening.
Give SOC and SAP teams the context needed to understand risk faster.
Move from raw alerts to prioritized findings and clearer next actions.