Blog
Never Trust, Always Verify: Why Zero Trust Is Key to Modern Cyber Defense
Author:
Jathin Das | Amit Kumar Sharma
Reading Time: 9 Minutes
Traditional security trusted anything inside the network perimeter. That assumption no longer holds. Remote work, cloud services, and mobile devices mean threats are just as likely to come from inside as outside. Zero Trust answers this by operating on one principle, which is to never trust and always verify. According to a Fortinet survey, 76% of organisations are adopting Zero Trust, up from 58% in 2021.
What Is Zero Trust?
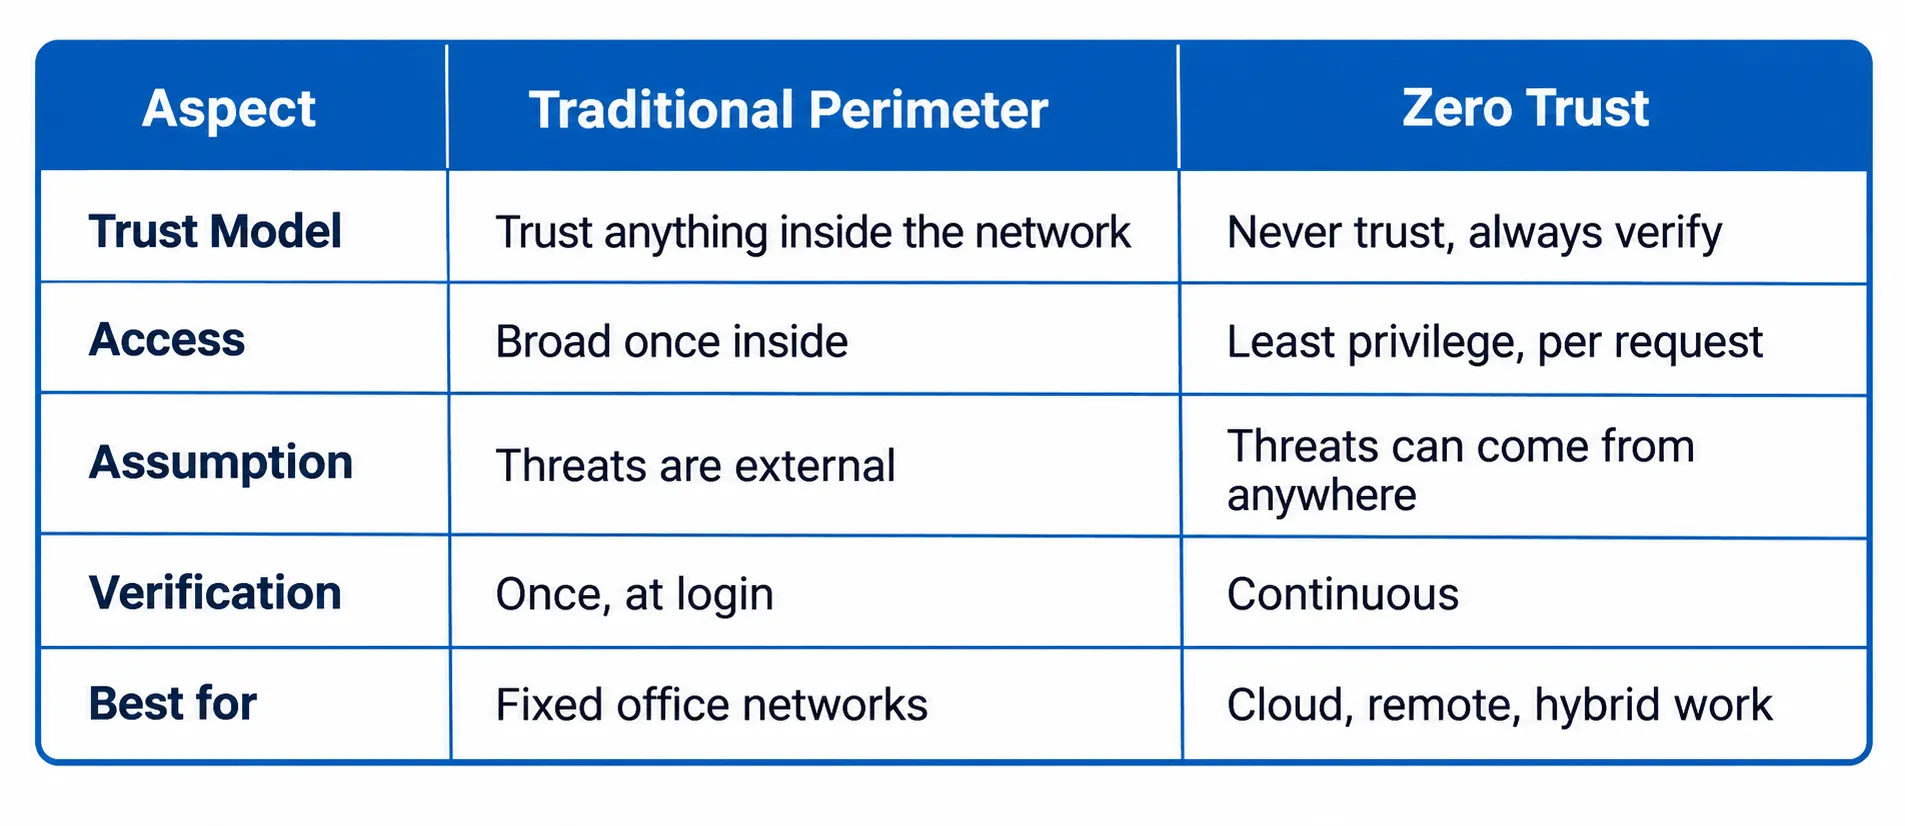
Zero Trust is a security model that removes automatic trust from users, devices, and applications. Every access request is verified based on identity, device health, and context before it is granted, whether it comes from inside or outside the network. Access is limited to only what each user genuinely needs, nothing more.
Zero Trust vs Traditional Perimeter Security
Perimeter security works like a walled building. Once inside, you are trusted to move freely. Zero Trust assumes the walls will eventually be breached, so it checks identity and permissions at every access point, every time. If an attacker steals one set of credentials, they still cannot roam freely across the network.
Core Principles of Zero Trust
Zero Trust rests on five principles:
- Verify explicitly: Authenticate every user and device on every request, not just at login.
- Least-privilege access: Give users only the access they need for the task at hand.
- Assume breach: Design as if attackers are already inside; contain the damage.
- Microsegmentation: Split the network so a breach in one area cannot spread laterally.
- Continuous monitoring: Keep checking identity, device health, and behaviour throughout each session.
Implementing Zero Trust
Successful implementation follows a few key steps.
Understand the architecture first. Map all users, devices, applications, and data flows before changing anything. It is impossible to identify where trust assumptions are currently baked in without this visibility.
Build a strong identity foundation. Identity management sits at the centre of Zero Trust. Invest in IAM solutions that support multi-factor authentication, single sign-on (SSO), identity governance, and identity federation. If identities are not trustworthy, nothing else in the model holds.
Use a phased approach. Start with high-risk areas or critical assets, then expand. An all-at-once rollout creates disruption and gaps. Starting small lets teams learn what works before scaling.
Integrate security tools. Combine IAM, endpoint security, network monitoring, and threat detection into a connected ecosystem. Siloed tools slow down detection and response; integration is what makes Zero Trust operational rather than theoretical.
Invest in employee education. Zero Trust changes how people access systems day to day. Staff need to understand why the model exists, what phishing looks like, and how to report suspicious activity. Buy-in matters; without it, workarounds appear fast.
The Future of Zero Trust
Zero Trust’s relevance will keep growing as hybrid work and cloud adoption expand. The model is built for environments where perimeter boundaries barely exist, and those boundaries are shrinking every year. Organisations that establish the identity foundation and continuous verification habits now will adapt faster when new attack surfaces appear, rather than scrambling to retrofit security onto an architecture that was never designed to handle them.
ABOUT AUTHOR
Frequently Asked Questions
Perimeter security trusts anyone inside the network. Zero Trust trusts no one by default and verifies every access request by identity, device health, and context, whether the request comes from inside or outside.
Start with your most critical assets or highest-risk access points. Build a strong identity foundation with MFA and SSO, then expand in phases. A gradual rollout limits disruption while you extend coverage across the network.
Verify explicitly, least-privilege access, and assume breach are the three foundational pillars. Microsegmentation and continuous monitoring support them in practice.

Protect your online assets from cyber threats with Paramount
Comprehensive cyber security solutions for individuals and businesses
Significantly reduce the risk of cyber threats and ensure a safer digital environment.
