 Your data is confidential and never shared
Why Post-Quantum
Cryptography Matters Now
Your data security strategy must account for how long information needs to remain confidential.

Public-key cryptography faces a new risk
A sufficiently powerful quantum computer could break RSA, elliptic curve cryptography, and Diffie-Hellman key exchange.

Stolen data can retain its value for years
Attackers can collect encrypted data today and decrypt it later, referred to as “harvest now, decrypt later.” PII, health records, government information, and customer data may need protection for years.
The standards are ready
NIST released its first PQC standards in August 2024: ML-KEM for key establishment, and ML-DSA and SLH-DSA for digital signatures.
Our Post-Quantum
Cryptography Services

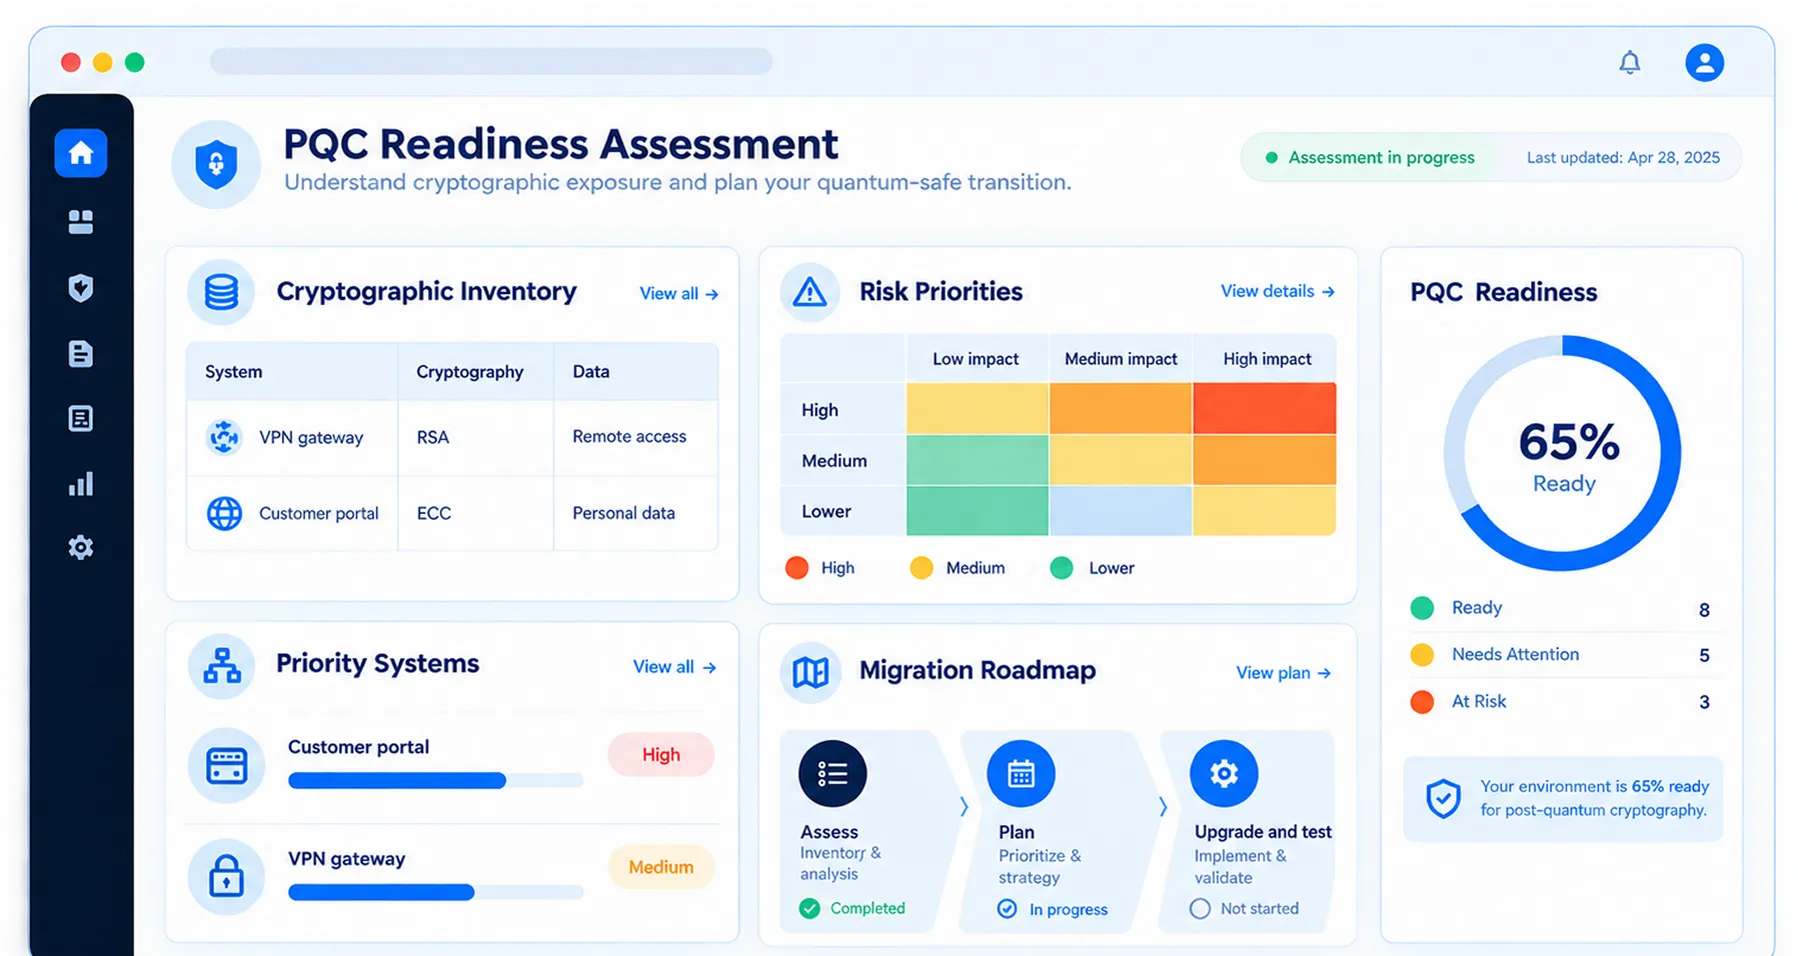
Cryptographic Discovery and Inventory
- Map cryptography across network security infrastructure and applications.
- Identify systems using algorithms vulnerable to quantum attacks.

Data Context Analysis
- Locate personal, health, government, and customer data across systems.
- Map the cryptography protecting each data store.

PQC Risk Assessment
- Classify assets through risk assessment: high, medium, or lower.
- Visualize exposure with heat maps and percentages.

Crown-Jewel Prioritization
- Identify the systems holding your most critical data.
- Prioritize changes by data sensitivity and business context.

Quantum-Resistant Algorithm Selection and Roadmap
- Recommend quantum-resistant algorithms and technologies suited to your environment.
- Sequence the changes in a phased roadmap.

Upgrade Support and Testing
- Support firewall, DLP, PKI, HSM, and Microsoft upgrades with vendors.
- Test changes. Scope penetration testing separately.
Systems Covered in a PQC
Readiness Assessment
Security architecture

Applications using encryption

Public and private keys

Data stores


CRM

VPNs

Internet banking

Firewalls

DLP

PKI

HSMs

Cloud environments and endpoint encryption
What You Receive From a
PQC Readiness Assessment
- Cryptographic inventory
- PQC-exposed assets and their share of the assessed inventory
- High, medium, and lower risk classifications
- Risk heat maps
- Priority crown-jewel systems
- Recommended algorithms and technologies
- Phased migration roadmap
- Infrastructure, security, and PKI upgrade recommendations
Why Choose Paramount for
Quantum-Resistant Encryption
The UAE Perspective
Government entities need transition plans
The UAE's National Encryption Policy and executive regulation call on government entities to develop formally approved plans for transitioning to post-quantum cryptography.
Cryptographic discovery is part of the national program
The Cyber Security Council's May 2026 agreement with ATRC supports scaling cryptographic discovery, inventory, and vulnerability assessment to help critical public and private sector entities plan their migration.
Paramount's perspective
[Approved expert quote explaining how UAE organizations can turn transition requirements into a prioritized migration plan, addressing vendor readiness and application dependencies.]
[Name]
[Designation], Paramount Assure
How Our PQC Migration Support Works

1. Assess
Establish where cryptography is used, what data it protects, and which exposures need attention first.

2. Plan
Match algorithms and technologies to each use case, then sequence changes around system and vendor dependencies.

3. Support and test
Work with your teams and vendors on agreed upgrades, then test the implemented changes.
Know Where Your PQC Assessment Should Start
Tell us which systems or data types you need to protect. Our SME will help you scope the assessment needed to understand their PQC exposure.
Your discussion will focus on
- Systems and applications to include
- Encryption, certificate, and key information to gather
- Owners who can support discovery
