Build AI Cybersecurity in the Right Order
A practical AI cybersecurity roadmap for Middle East organizations to move from secure foundations to governed AI adoption.


Secure Your Business with AI Cybersecurity
 Your data is confidential and never shared
Why defense AI needs a roadmap
Adopting AI solutions without a roadmap creates more risk than readiness
When teams incorporate AI solutions in silos, security leaders lose a clear view of what is being used, what data it touches, who controls it, and how risk is governed.

Disconnected tools
AI tools are often purchased for individual teams, use cases, or vendors. However, they do not share security controls.

Duplicated spend
Multiple teams may buy similar AI capabilities without a shared roadmap. Budgets get spread across overlapping tools.

Unclear control
Leaders may not have a consistent view of who can use AI, what data it can access, or which actions need human approval.

Weak data readiness
Fragmented, unclassified, or poorly protected data makes AI outputs harder to verify and harder to govern.
The Roadmap
Secure AI adoption starts by knowing what comes first
Scaling AI safely is not about buying the most advanced tool first. It starts by building the security foundation, then moving AI into controlled workflows, and only then preparing for trusted autonomy.
Paramount's Three Horizons model breaks that journey into three practical stages.
Secure the
foundation
Build the data, cloud, access, and governance base AI solutions needs before it can be trusted.
Move AI into
controlled work
Use AI assistants to prepare outputs and support teams while people stay in control.
Prepare for
trusted autonomy
Define the rules, limits, supervision, and audit trails before AI can act at speed.
Horizon 1: Making AI safe to use
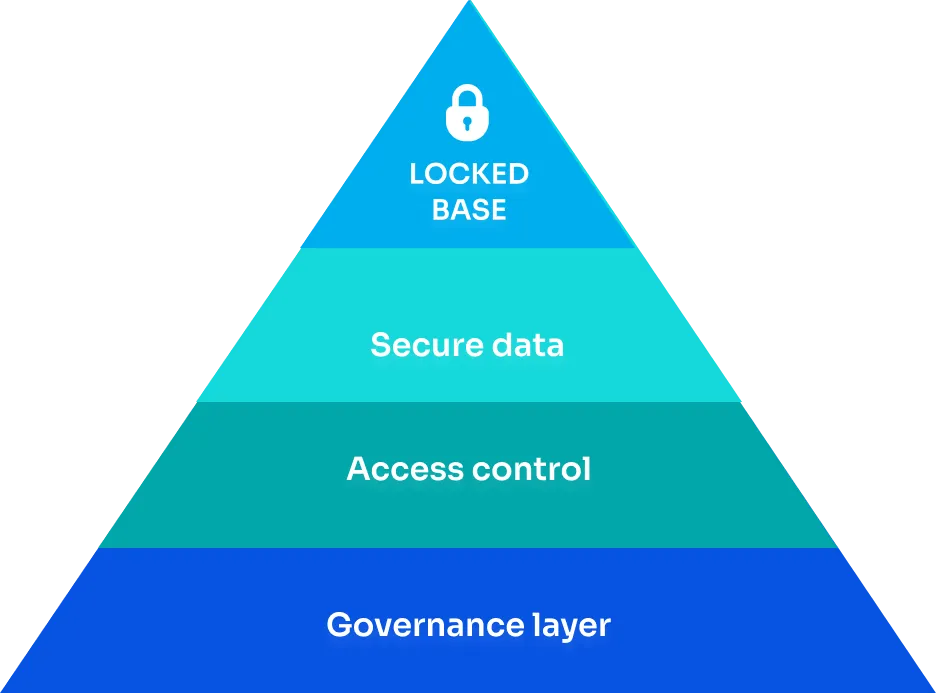
AI readiness begins with the data layer
AI cybersecurity depends on the quality, security, and governance of the information underneath it. Before organizations scale AI tools, they need a data layer that is clean, protected, and controlled.
Foundation visual
Secure data environment
Operational data is cleaned, classified, stored, and protected inside controlled environments.
Controlled access
Users, systems, and AI tools only reach the data they are authorized to use.
Governance by design
Usage policies, approval routes, logging, and accountability are defined before AI scales.
Horizon 2: Making AI Useful in Daily Work
AI becomes useful when it can work through approved context
Once the data layer is controlled, AI can support daily cybersecurity work by finding context, preparing outputs, and routing decisions through human approval.
1
Task given
The user gives the AI a clear operational goal.
2
Context gathered
The AI searches approved internal sources and pulls together relevant information.
3
Options prepared
The AI drafts briefs, compares signals, summarizes risks, or prepares next steps.
4
Human approval
A person approves, rejects, or redirects before anything moves forward.
Horizon 3: Making AI Autonomous
Move from human-led workflows to governed autonomy
Cybersecurity teams can use AI for faster response only when the operating limits are defined first. That means clear permissions, human supervision, intervention controls, and full traceability.
AI System
Comparison
See where your AI cybersecurity model stands today
Each horizon changes what AI can do, what teams need to govern, and how much control must be built into the operating model.
Purpose
Tools
Control
Timing
Horizon 1:
Foundation
Get the foundation right
Secure cloud + approved AI
People work, AI assists
Now
Horizon 2:
Operational AI
Do everyday work faster
AI assistants / agents
People lead, AI prepares
Soon
Horizon 3:
Trusted Autonomy
Act at high speed
Autonomous systems
AI acts, people supervise
Future
Why Paramount
Is your cybersecurity environment ready for AI?
Paramount helps Middle East organizations assess their data, security, and governance readiness before scaling AI across cybersecurity workflows.
15+
Customers trust Paramount with cybersecurity challenges
575+
Cybersecurity and technology experts
35+
Of the GCC's biggest banks supported
30+
Government customers across the region
Find your starting point in the Three Horizons
Assess your data, security, and governance readiness before scaling AI across defense workflows.
FAQs
Clear answers for teams deciding whether Paramount is the right cybersecurity partner to engage.
Start by checking four areas: where your security data sits, who can access it, which AI tools are already in use, and whether outputs can be logged or reviewed. If these are unclear, AI should stay in assisted workflows before moving closer to automation.
Create a shared AI cybersecurity roadmap before tool selection. Security, IT, risk, and business teams should agree on approved use cases, data access rules, vendor requirements, and ownership before new AI tools are added.
A useful review should map current AI tools, data exposure, identity controls, governance gaps, monitoring coverage, and automation risks. The output should show what to fix now, what can move into controlled AI workflows, and what is not ready for autonomy.
Secure the data layer first. That means classification, identity-based access, approved repositories, monitoring, and clear rules for what AI tools can read, generate, store, or share.
AI should take action only when the task is low-risk or pre-approved, the action limits are defined, a human override exists, and every action is logged. Anything involving sensitive data, privilege changes, or incident response decisions needs stronger approval controls.
